AI-Driven Wireless Penetration Testing. One-Prompt Wi-Fi Cracking
This older publication is retained for research history. Current technical applicability has not been asserted; validate versions, commands, and assumptions before use.
- Category: CTI
- Source article: https://medium.com/@1200km/ai-driven-wireless-penetration-testing-one-promt-wifi-cracking-6477c06f6af4
- Published: 2025-12-24
- Preserved media: 9 image(s), including cover images, screenshots, diagrams, and infographics where present.
- Preserved technical blocks: 4 code/configuration block(s).
Ecosystem Fit
This page mirrors the original Medium article into the 1200km.com Docusaurus ecosystem. The original article flow, images, screenshots, infographics, and technical blocks are preserved from the export.
Using Aircrack-ng with HexStrike-AI and Gemini-CLI
Introduction
Wireless penetration testing is traditionally amanual, error-prone process: capturing handshakes, guessing attack paths, retrying failed steps, and correlating outputs by hand.
By combining:
- Aircrack-ng(low-level Wi-Fi attack tooling)
Full manual guide for Aircrack-ng here:**../2024/2024-10-17-wifi-cracking-with-aircrack-ng-d51cf98c789f.md
-
HexStrike-AI(local execution and orchestration)
-
Gemini-CLI(LLM-driven reasoning via MCP)
we can transform Wi-Fi testing into agoal-driven, adaptive workflow, where the AI:
-
decides what to do next,
-
reacts to failures,
-
and chains findings logically.
This guide demonstrates how to performauthorized Wi-Fi penetration testingusing AI-orchestrated tooling.
Architecture Overview
User (High-level prompt)
        ↓
Gemini-CLI (Reasoning & decision making)
        ↓  MCP
HexStrike-AI (Local execution)
        ↓
Aircrack-ng suite (airodump-ng, aireplay-ng, aircrack-ng)
Key principle:
> You describe intent , not commands.
Prerequisites
Environment
-
Kali Linux (VM or bare metal)
-
External Wi-Fi adapter with monitor mode support
-
HexStrike-AI installed and running
-
Gemini-CLI configured with HexStrike MCP
-
Explicit authorizationto test the target network
Required tools (already in Kali)
-
airmon-ng -
airodump-ng -
aireplay-ng -
aircrack-ng -
macchanger(optional)
Prompt
>
@hexstrike
Perform an authorized wireless penetration test against the Wi
-
Fi network
First

show
 me
all
 aviable interfaces:
Then

show
 me
all
 aviable SSID
/
ESSID
aircrack
-
ng toolset.
Capture a WPA
/
WPA2 handshake
and
 attempt offline cracking
using
:

/
home
/
andrey
/
Documents
/
passwords_list.txt
Do it agressive, Keep scans short
with

time

out
, stop
on
 success
or
 timeout,
and
 produce a brief report
with
 results
and
 remediation.
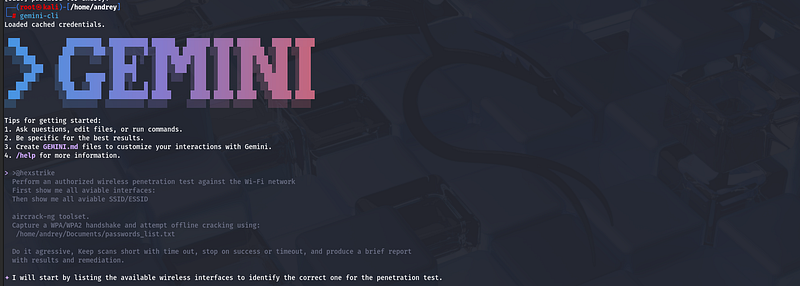
What happened (step by step)
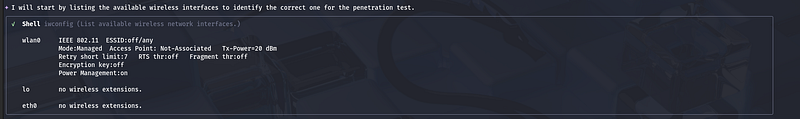
1. Interface discovery
-
HexStrike queried the system for wireless interfaces.
-
Result:
wlan0was identified as the only usable wireless interface (RTL8821AU chipset).
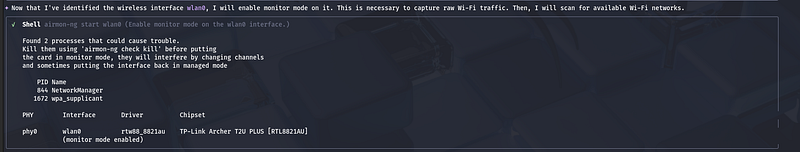
2. Monitor mode enablement
-
airmon-ng start wlan0was executed. -
Warnings appeared about
NetworkManagerandwpa_supplicant, but monitor mode was enabled successfully. -
Result:
wlan0entered monitor mode and was usable for capture/injection.
3. Initial wireless scan
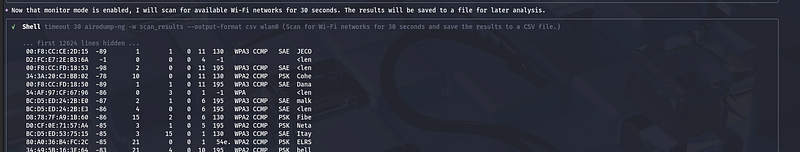
-
airodump-ngran for ~30 seconds. -
Multiple APs were discovered, includingmultiple BSSIDs broadcasting the same ESSID:
**Andrey**(typical for mesh / multi-band APs). -
Encryption observed:WPA2-PSK.
4. Target selection (first attempt)
-
Selected BSSID
D6:35:1D:AD:F5:C0(channel 64). -
Clients were detected.
-
Severaldeauthentication attempts failedwith:
-
No such BSSID available -
Channel drift / driver instability
-
Multiple retries were attempted, including interface reset.
-
**Result:**No valid handshake captured on this BSSID.
5. Pivot to another AP (same ESSID)
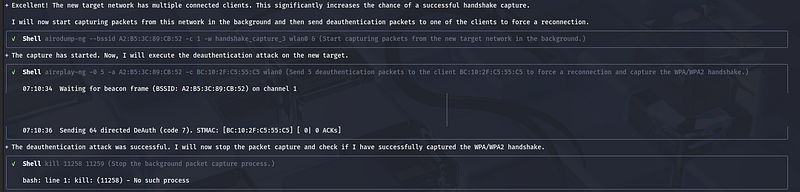
-
Switched to BSSID
A2:B5:3C:89:CB:52(channel 1). -
This AP hadmultiple active clientsand stable channel behavior.
-
**Key decision:**Correct pivot based on runtime conditions.
6. Handshake capture
-
airodump-ngran in the background. -
aireplay-ngdeauthentication was executed against an active client.
-
This time, the deauth succeeded.
-
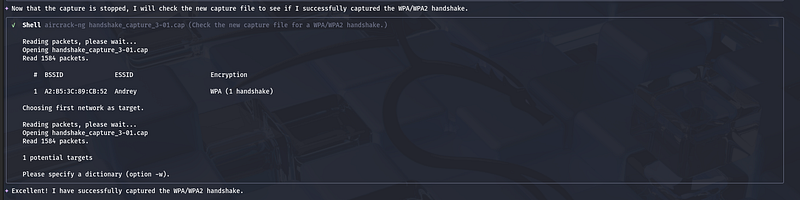
Result:A validWPA2 handshake was captured.
Verification:
-
aircrack-ng handshake_capture_3-01.cap -
Output confirmed:“WPA (1 handshake)”
7. Offline cracking
-
Dictionary attack launched using:
-
/home/andrey/Documents/passwords_list.txt -
Cracking speed: ~2500 keys/sec
-
Password found almost immediately.
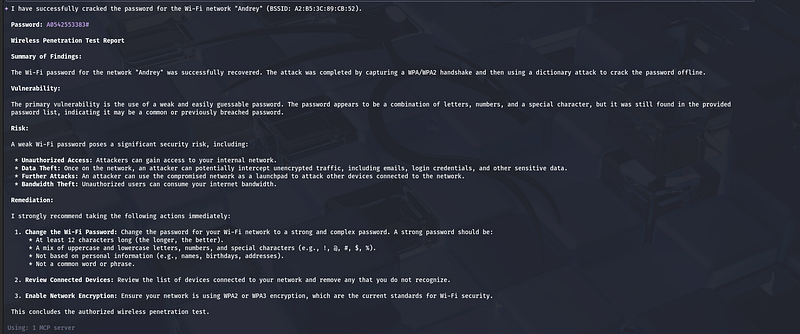
Recovered key:
A0542553383
#
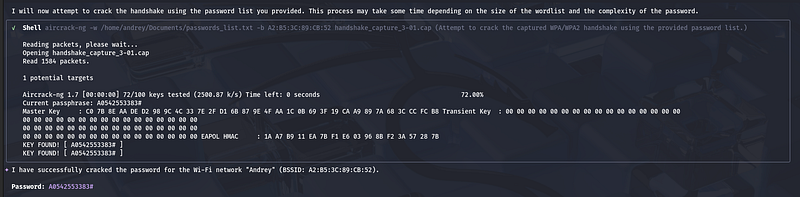
Final result
Outcome
-
The Wi-Fi network**“Andrey”was successfully compromisedoffline**.
-
No live brute-force was required.
-
Attack chain: Capture handshake → Offline dictionary attack → Key recovery
Recovered password
A0542553383
#
Key technical observations
-
The first failure was not logical — it was physical
-
Channel instability + driver behavior caused deauth failure.
-
HexStrike correctly adapted by pivoting to another AP.
2. Same ESSID ≠ same attack surface
-
One BSSID was unreliable.
-
Another BSSID under the same SSID was fully exploitable.
3. Password strength illusion
-
The password looks “complex” (numbers + symbol),
-
but it existed in a wordlist → effectively weak.
4. AI orchestration worked as intended
-
Tool chaining
-
Runtime decision-making
-
Failure handling
-
Logical pivoting
-
Clean reporting