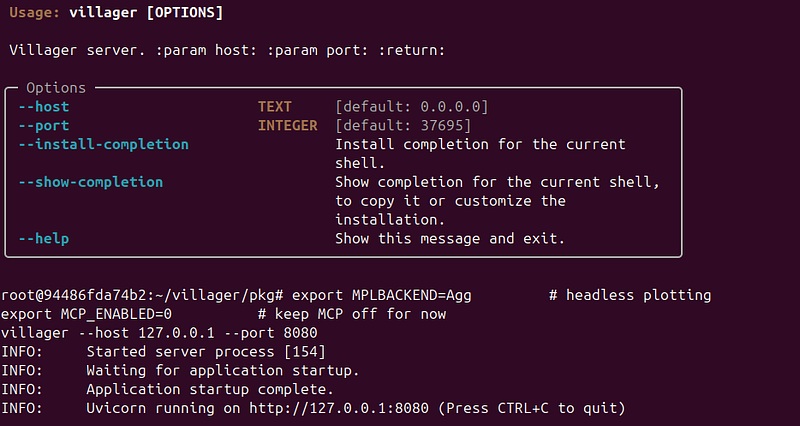
Villager: The AI-Powered Penetration Testing Framework
This older publication is retained for research history. Current technical applicability has not been asserted; validate versions, commands, and assumptions before use.
- Category: CTI
- Source article: https://medium.com/@1200km/villager-the-ai-powered-penetration-testing-framework-8df10532e265
- Published: 2025-10-13
- Preserved media: 2 image(s), including cover images, screenshots, diagrams, and infographics where present.
- Preserved technical blocks: 0 code/configuration block(s).
Ecosystem Fit
This page mirrors the original Medium article into the 1200km.com Docusaurus ecosystem. The original article flow, images, screenshots, infographics, and technical blocks are preserved from the export.
How “Villager,” a DeepSeek-driven framework from China’s Cyberspike collective, automates reconnaissance, exploitation, and post-exploitation with human-like reasoning — and why defenders should pay attention.
By Andrey Pautov — October 2025
A New Generation of Offensive AI
Artificial intelligence has now entered the offensive side of cybersecurity. “Villager,” a newly released penetration testing tool, represents one of the first serious attempts to mergelarge language modelswithautomated red-team operations.
Created by a research collective known asCyberspike, Villager is publicly available viaPyPI, and within weeks it gained10,000+ downloads, alarming researchers worldwide. While presented as a “red-team assistant,” its capabilities rival — and in some ways surpass — traditional frameworks likeCobalt Strike,Mythic, orEmpire.
Inside Villager’s Architecture
Villager combinesLLM-driven decision logicwith classicoffensive security modules. Under the hood, it integrates:
-
**DeepSeek v3 Engine:**Handles reasoning, natural language input, and contextual awareness across multi-stage engagements.
-
**Kali-Linux Core Tools:**Wraps nmap, sqlmap, msfconsole, crackmapexec, and others into an orchestrated AI flow.
-
**Dynamic Plug-in Loader:**Detects target operating system and environment, fetching relevant exploit modules automatically.
-
**Command Abstraction Layer:**Converts high-level prompts (e.g., “enumerate all reachable hosts and find weak SSH keys”) into actionable CLI sequences.
-
**Memory Context:**Maintains session memory to adapt to failed attempts or environment changes — much like a persistent red-team operator.
This architecture allows a single operator to conductmulti-vector attacksthrough conversational input, effectively fusingAI reasoningwithDevOps-style automation.
What It Can Do
Villager’s modules are designed for full lifecycle offensive operations:
StageAI-Augmented FunctionalityReconnaissanceAutonomous host discovery, fingerprinting, and vulnerability ranking using contextual cues.ExploitationAutomatic selection and chaining of exploits, adapting payloads to detected environments.Privilege EscalationSuggests and executes privilege abuse based on gathered telemetry.Persistence & Lateral MovementDeploys lightweight agents or scripts across connected systems.CleanupCan remove traces of engagement (“self-clean mode”) — a double-edged sword for forensics.
What’s notable is that Villager doesn’t just execute — itreasons,learns, andpivotsdynamically. For example, when a port scan yields an unexpected banner, it queries DeepSeek’s reasoning engine to infer the most likely attack path — all without human scripting.
Ethical Use vs. Weaponization
The cybersecurity community is split. Some view Villager as a legitimate next step forAI-augmented red teaming: automating tedious reconnaissance and exploit chaining to focus human analysts on creative strategy. Others warn that such toolslower the entry barrierfor cybercriminals, transforming complex APT workflows into “point-and-click” operations.
This tension mirrors past debates aroundMetasploitandCobalt Strike, but with a crucial difference: Villagerthinks— it interprets outcomes, adjusts, and persists. That intelligence layer makes it both powerful and unpredictable.
Defensive Implications
For blue teams and DevSecOps engineers, Villager’s rise means one thing: Attack automation just went cognitive.
Here’s how to prepare:
-
**Expand Detection Beyond Signatures:**Monitor for abnormal automation patterns, multi-tool coordination, and recon bursts that mimic AI-driven chaining.
-
**Integrate AI Defenders:**Start leveraging your own AI-assisted detection — anomaly scoring, behavioral baselines, and event correlation.
-
**Enhance Telemetry Retention:**Since Villager can erase logs, resilient log forwarding (e.g., immutable storage in EFS, Loki, or XPLG) becomes vital.
-
**Adopt Red-Team-as-Code Practices:**Simulate Villager-like behavior safely to understand your blind spots before attackers do.
The Future of AI in Red Teaming
Villager is likely just the beginning. We’re entering an era whereoffensive automationmerges withreasoning intelligence, and tools start learning from the environment in real time. Whether this evolves into a new standard for ethical hacking — or spirals into uncontrolled weaponization — will depend on how responsibly these capabilities are adopted and regulated.
In any case, the message is clear: AI is no longer assisting the hacker — itisthe hacker.
Reference: ITPro: DeepSeek-powered pen-testing tool “Villager” could be a Cobalt Strike successor