Geographic / ASN
Atlas home · Research path · Operational families · Anomaly models · Visual index
Consolidated 27 September 2026 from the revised publication. Source-reported incidents, proposed models, functional tests, and synthetic results remain separate evidence classes. Provenance and review scope.
A change in the network/location context associated with an identity.
Telemetry contract: Sign-in/VPN records, device context and versioned IP/ASN/geolocation enrichment.
Candidate method [unvalidated until tested]: Compare the account and device history; treat geolocation as uncertain and account for VPN/proxy egress.
Benign alternatives and limits: Mobile networks, privacy relays, travel and shared egress can create apparent impossible travel.
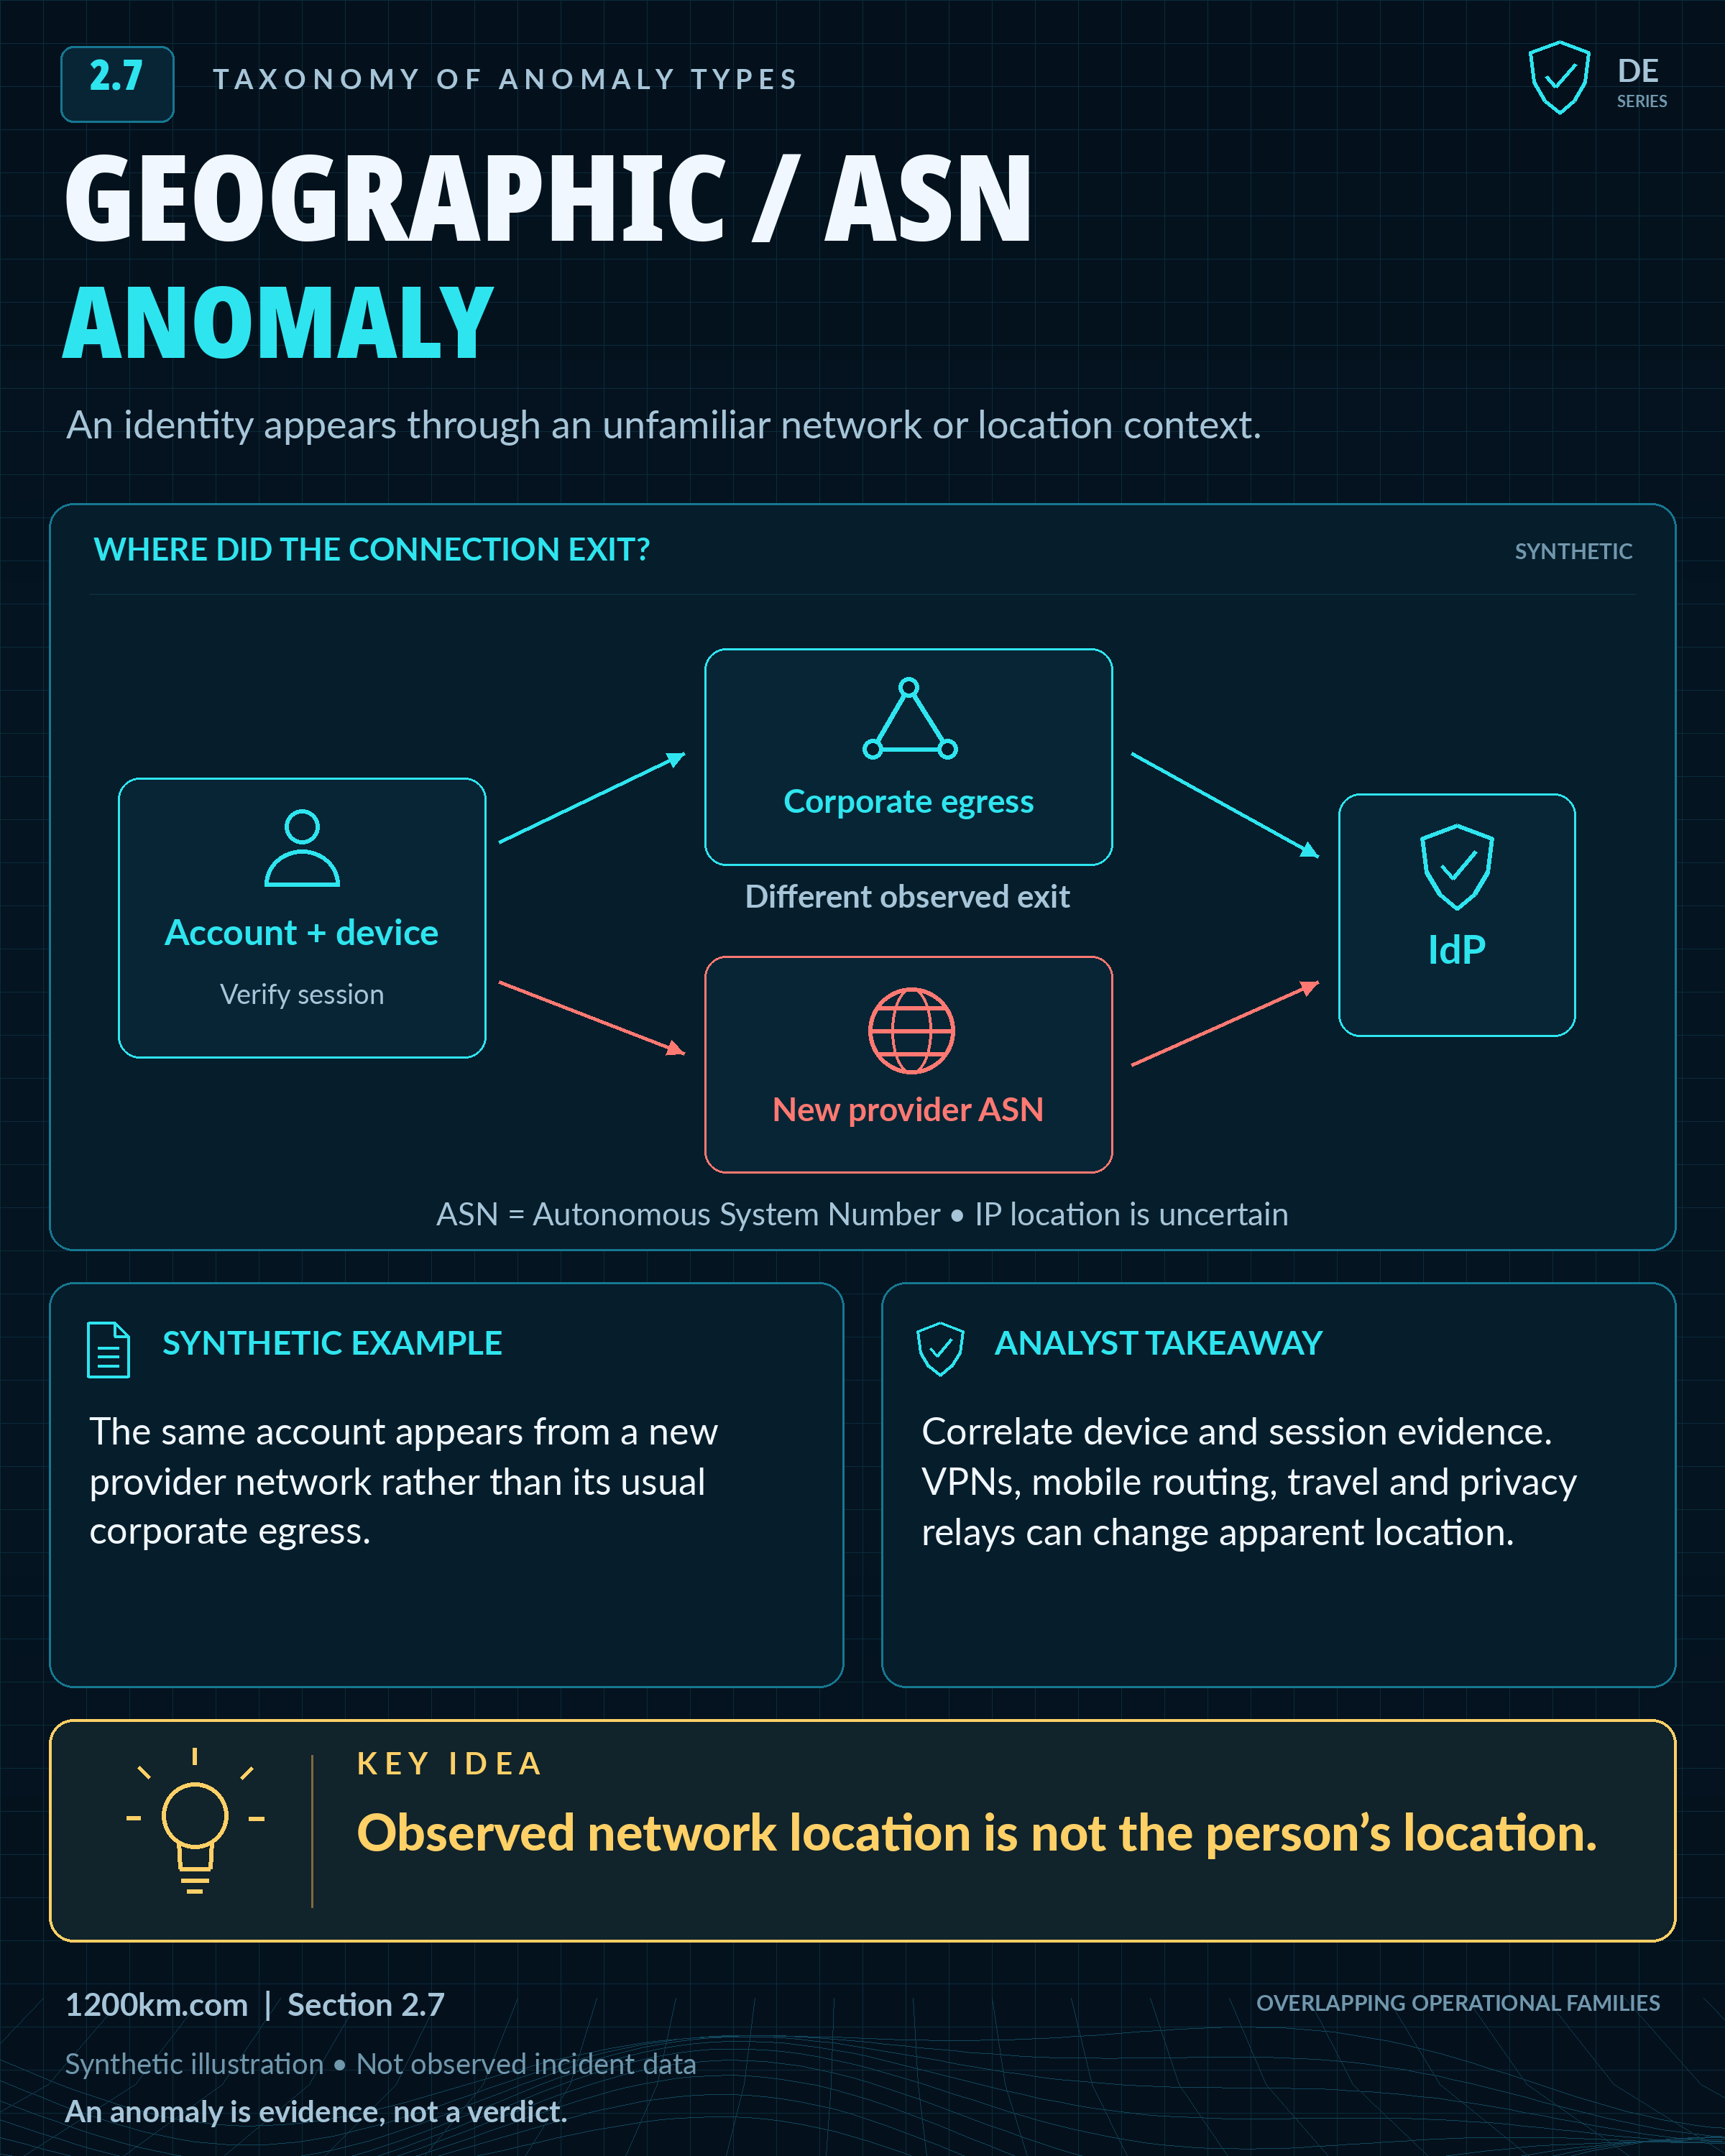
Text equivalent and full-size diagram
IP geolocation is not a measurement of the person’s physical location.
The account and device can appear through corporate egress or a new provider network before reaching the identity provider.
ASN means Autonomous System Number. Observed source-IP location is uncertain and need not be the person’s location.
Correlate device and session evidence; VPNs, mobile routing, travel and privacy relays can change the apparent exit.
Evidence tags: Identity and access · Network telemetry · Cloud and SaaS. Statistical forms: contextual.
Browse articles and guides: Geographic / ASN.
Reported incidents and detection interpretations
UNC5537 and Snowflake customer data theft
Period: 2024. Evidence: campaign reported by the cited source.
Observed [source-reported]: Mandiant observed VPN-origin access and separate VPS infrastructure associated with exfiltration in the Snowflake customer campaign. Mandiant: UNC5537 Targets Snowflake Customer Instances for Data Theft and Extortion.
Anomaly interpretation [inferred]: Compare source networks with each account's approved access paths and subsequent queries. ASN category is context, not an identity or maliciousness verdict.
Telemetry to validate: Snowflake login history, timestamped IP/ASN enrichment, query history and destination ownership.
Boundary / competing explanation: VPNs are common legitimate infrastructure. Neither a country nor an ASN identifies the human operator.
ATT&CK [author-mapped behavior, not actor attribution]: T1078.004 — Valid Accounts: Cloud Accounts
Midnight Blizzard compromise of Microsoft
Period: Reported January 2024. Evidence: incident reported by the cited source.
Observed [source-reported]: Midnight Blizzard used residential proxies also used by legitimate customers, reducing the usefulness of static IP indicators. Microsoft: Midnight Blizzard: Guidance for responders on nation-state attack.
Anomaly interpretation [inferred]: Evaluate unfamiliar sign-in properties and source diversity alongside the account's behavior. Residential-looking traffic can conceal an intrusion.
Telemetry to validate: Historical sign-in properties, IP/ASN observations, device and application context.
Boundary / competing explanation: Impossible-travel logic is vulnerable to VPN and proxy artifacts; no fixed travel threshold is asserted here.
ATT&CK [author-mapped behavior, not actor attribution]: T1110.003 — Brute Force: Password Spraying
Crosslinks: Frequency / Rate · Identity / Access. Statistical foundation in the Anomaly Detection Atlas. Related research: Detecting Malicious Insider Activity: A Technical Detection Engineering Guide.
Illustrative scenarios (not additional incidents):
-
A user who has only ever logged in from Israel suddenly authenticates to Microsoft 365 from Vietnam and then accesses sensitive SharePoint content minutes later.
-
An administrator signs in from a residential ISP in the morning and then appears from a cloud-hosting ASN in another country 25 minutes later, triggering impossible-travel logic.
-
A service account that normally uses one fixed corporate VPN egress suddenly accesses the cloud console from a consumer mobile network ASN.
-
A SaaS account with a stable history of logins from one city begins showing repeated access from multiple distant countries over two days.
-
A privileged user who normally connects only through a known enterprise VPN starts logging in from a newly observed anonymization provider or VPS-hosting ASN.
Apply this analytical view
These are curated conceptual links, not claims that a specific model detected the cited incidents.
Models: Valid credentials used from an unexpected context · External remote-service session.
Collection references: User Account Authentication · Logon Session Metadata · Network Traffic Flow. These describe data components, not equivalent connectors or guaranteed fields.
Technique workspaces
Follow the exact technique ID to source rules, associated tools, collection references, and documented lab candidates. A navigation association is not live validation.