Certificates
Purpose
Use TLS certificate data as one feature in infrastructure clustering.
Practitioner-Level Explanation
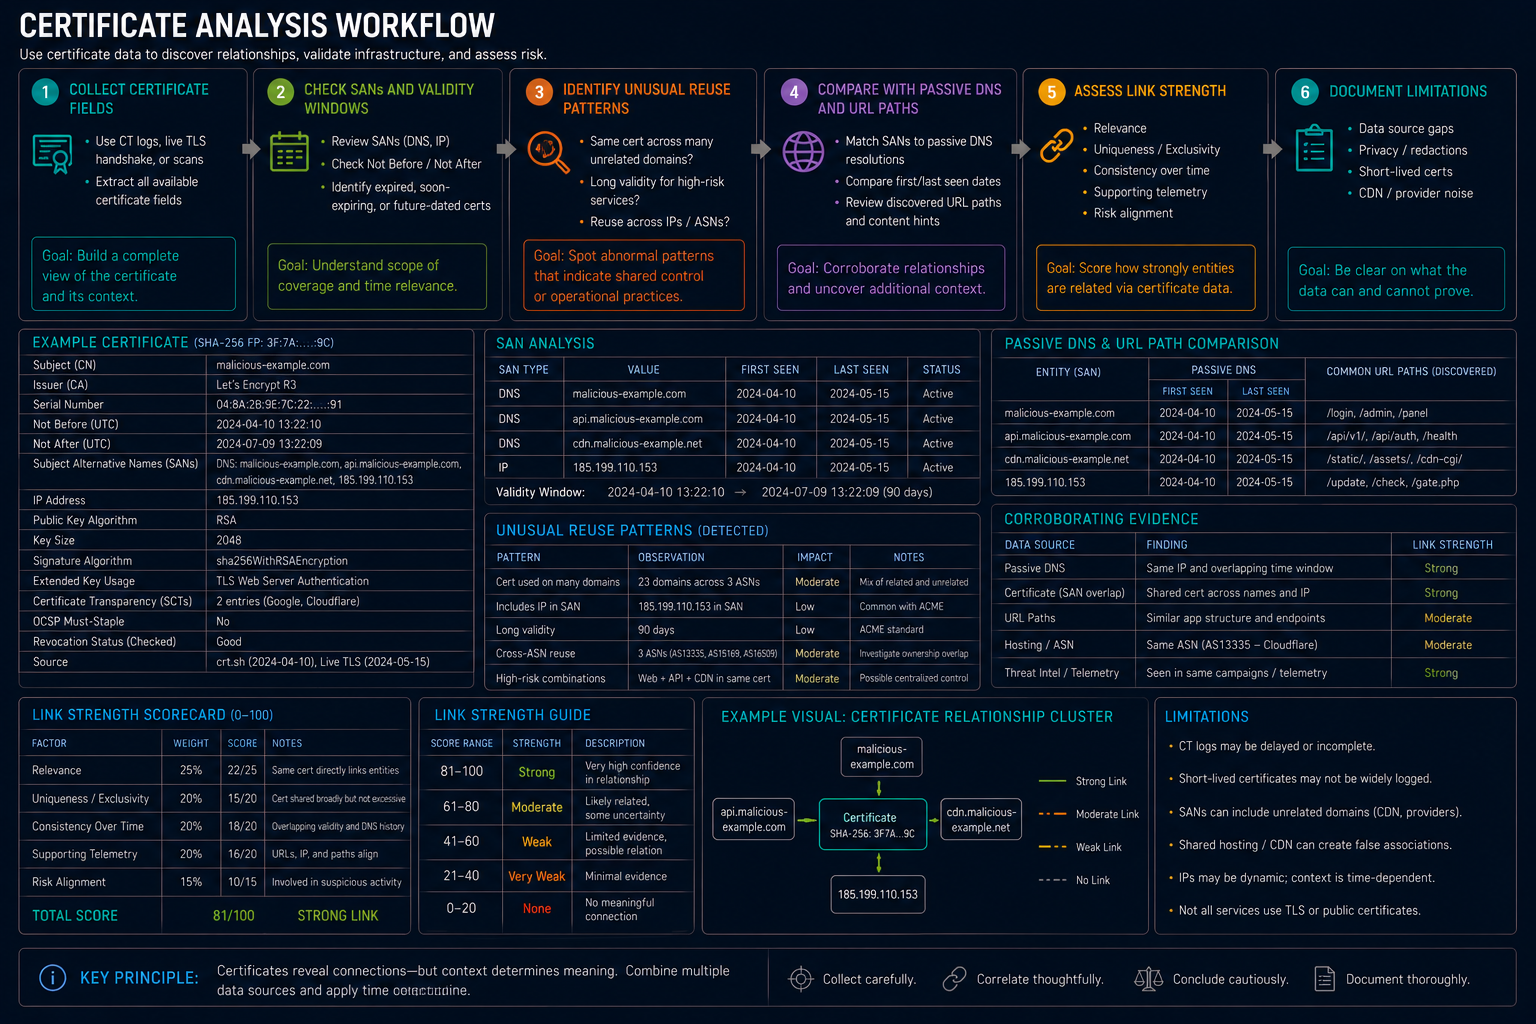
Certificates can reveal domain relationships through subjects, issuers, SANs, serials, validity windows, and reuse patterns. Certificate pivots are stronger when the certificate is unusual, reused across a small set, and temporally aligned with activity.
They are weaker when using automated certificates, common issuers, or shared hosting platforms.
CTI Relevance
Certificate pivots support infrastructure clustering, detection enrichment, and timeline reconstruction.
Common Mistakes
- Pivoting on common certificate issuers.
- Ignoring automated certificate churn.
- Treating certificate reuse as actor identity.
- Not checking validity dates.
Practical Workflow
- Collect certificate fields.
- Check SANs and validity windows.
- Identify unusual reuse patterns.
- Compare with passive DNS and URL paths.
- Assess link strength.
- Document limitations.
Example / Mini Case
Two domains share a rare certificate subject and appeared within the same week. That is a moderate pivot if supported by similar URL paths or payload behavior. It is weak if both use common managed hosting and no other overlap exists.
Analyst Checklist
- Are certificate fields specific enough?
- Are validity dates aligned?
- Is reuse rare or common?
- Is there corroboration beyond the certificate?
Output Artifact
Certificate Fingerprint:
Subject:
Issuer:
SANs:
Validity:
Related Domains:
Rarity:
Corroboration:
Assessment: