Evidence Strength Ladder
Purpose
Rank attribution evidence by strength and limitations.
Practitioner-Level Explanation
Not all attribution evidence has equal weight. A reused IP address is weak by itself. A unique malware build, exclusive infrastructure, operator mistake, and corroborated victimology together are stronger.
The ladder helps analysts explain why a judgment is high, medium, or low confidence.
CTI Relevance
Evidence weighting prevents overclaiming and makes attribution review possible.
Common Mistakes
- Treating all overlaps as equal.
- Ignoring time windows.
- Not checking whether infrastructure is shared.
- Overweighting victimology.
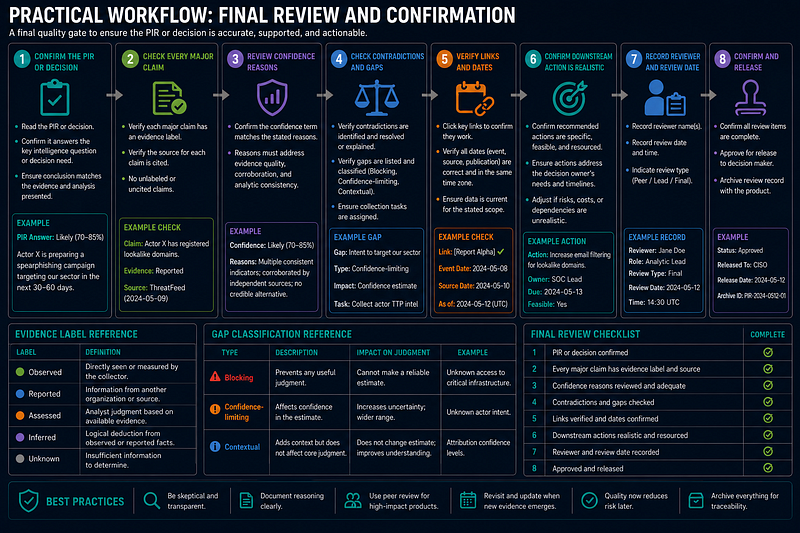
Practical Workflow
- List evidence items.
- Classify each item by type.
- Assess exclusivity and timing.
- Identify benign or alternative explanations.
- Combine evidence only when relationships are valid.
- Document confidence impact.
Example / Mini Case
Weak evidence: same cloud provider, common tool, generic phishing theme. Stronger evidence: unique C2 path pattern, malware configuration overlap, repeated operator schedule, and corroborated targeting pattern.
Analyst Checklist
- Is the evidence exclusive?
- Is timing aligned?
- Could infrastructure be shared or resold?
- Does the evidence identify actor, tool, or only activity cluster?
Output Artifact
Evidence Item:
Type:
Strength: Weak / Moderate / Strong
Timing:
Exclusivity:
Alternative Explanation:
Confidence Impact:
Source:
Cross-Links
- Attribution Methodology
- Confidence vs Probability
- Infrastructure Pivoting Limitations
- Israel CTI — Scoring Models
- Israel CTI — Actor Workbench