Intelligence to Detection
Purpose
Convert CTI claims into telemetry requirements, hunts, detections, SOC actions, and validation plans.
Practitioner-Level Explanation
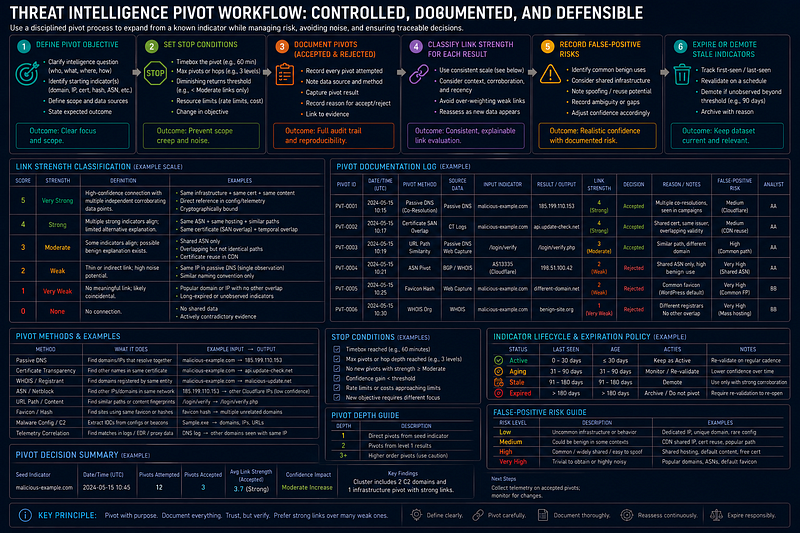
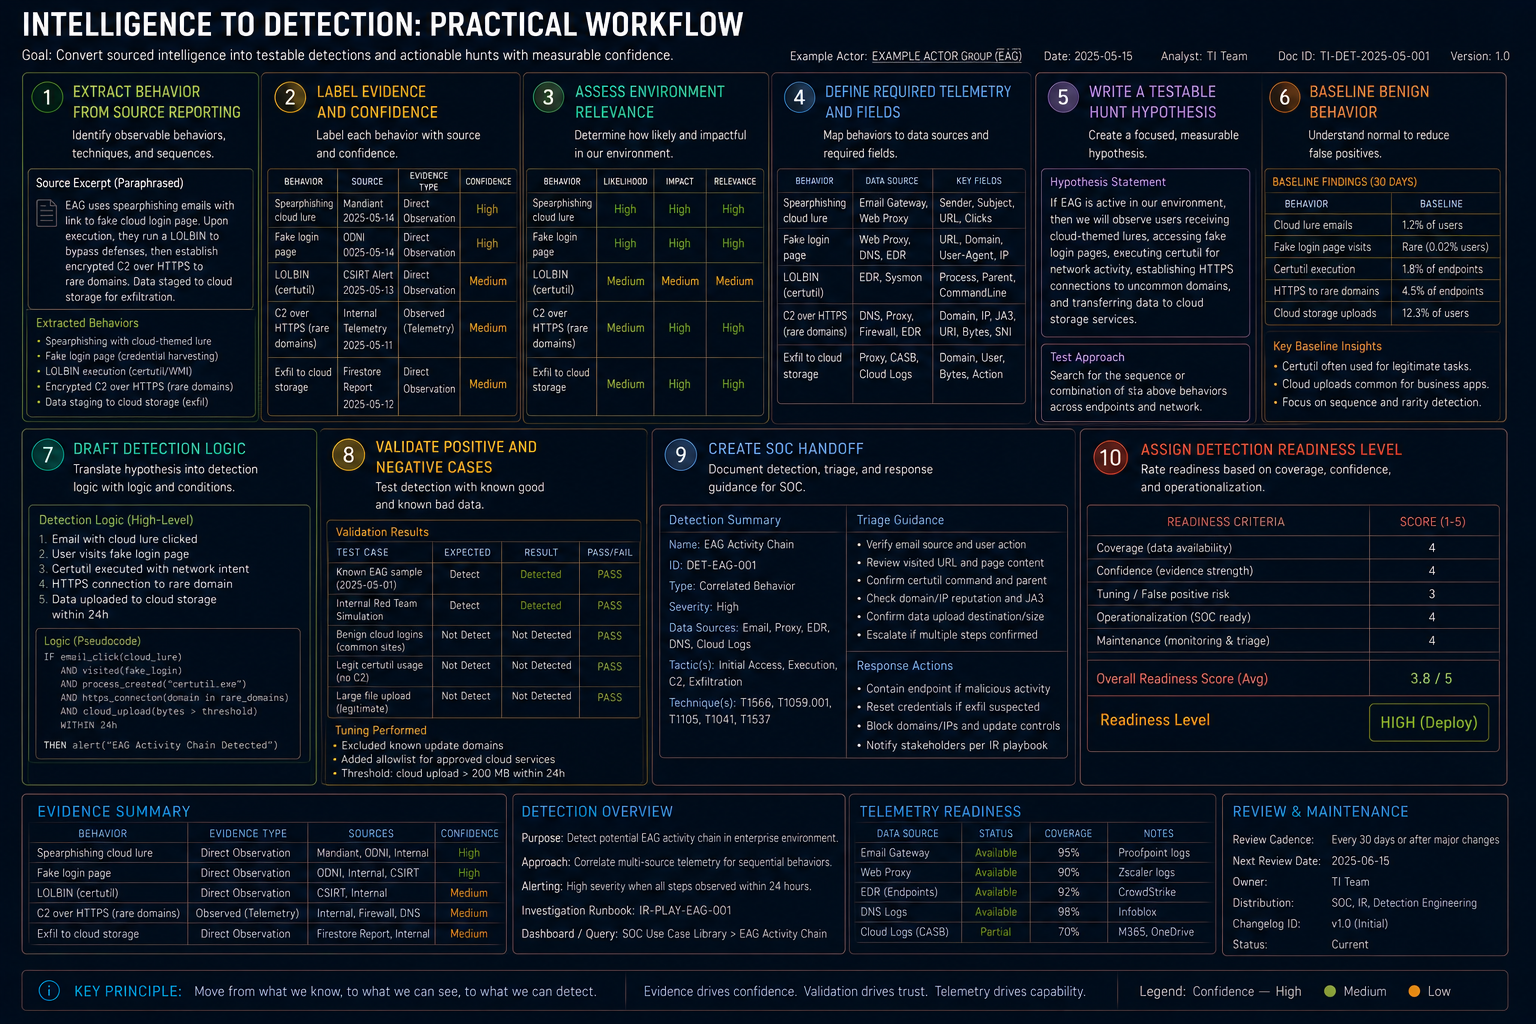
CTI-to-detection is a chain, not a single translation step; the Customer project turns that chain into delivery gates. A source reports behavior. The analyst labels evidence, assesses relevance, identifies telemetry, writes a hunt hypothesis, validates false positives, and only then promotes detection logic.
The actor name is usually less important than the behavior and observable; use the Israel CTI Actor Workbench only after evidence is labeled.
CTI Relevance
This workflow is the bridge between CTI and operational defense. It makes intelligence useful to detection engineering and SOC teams.
Common Mistakes
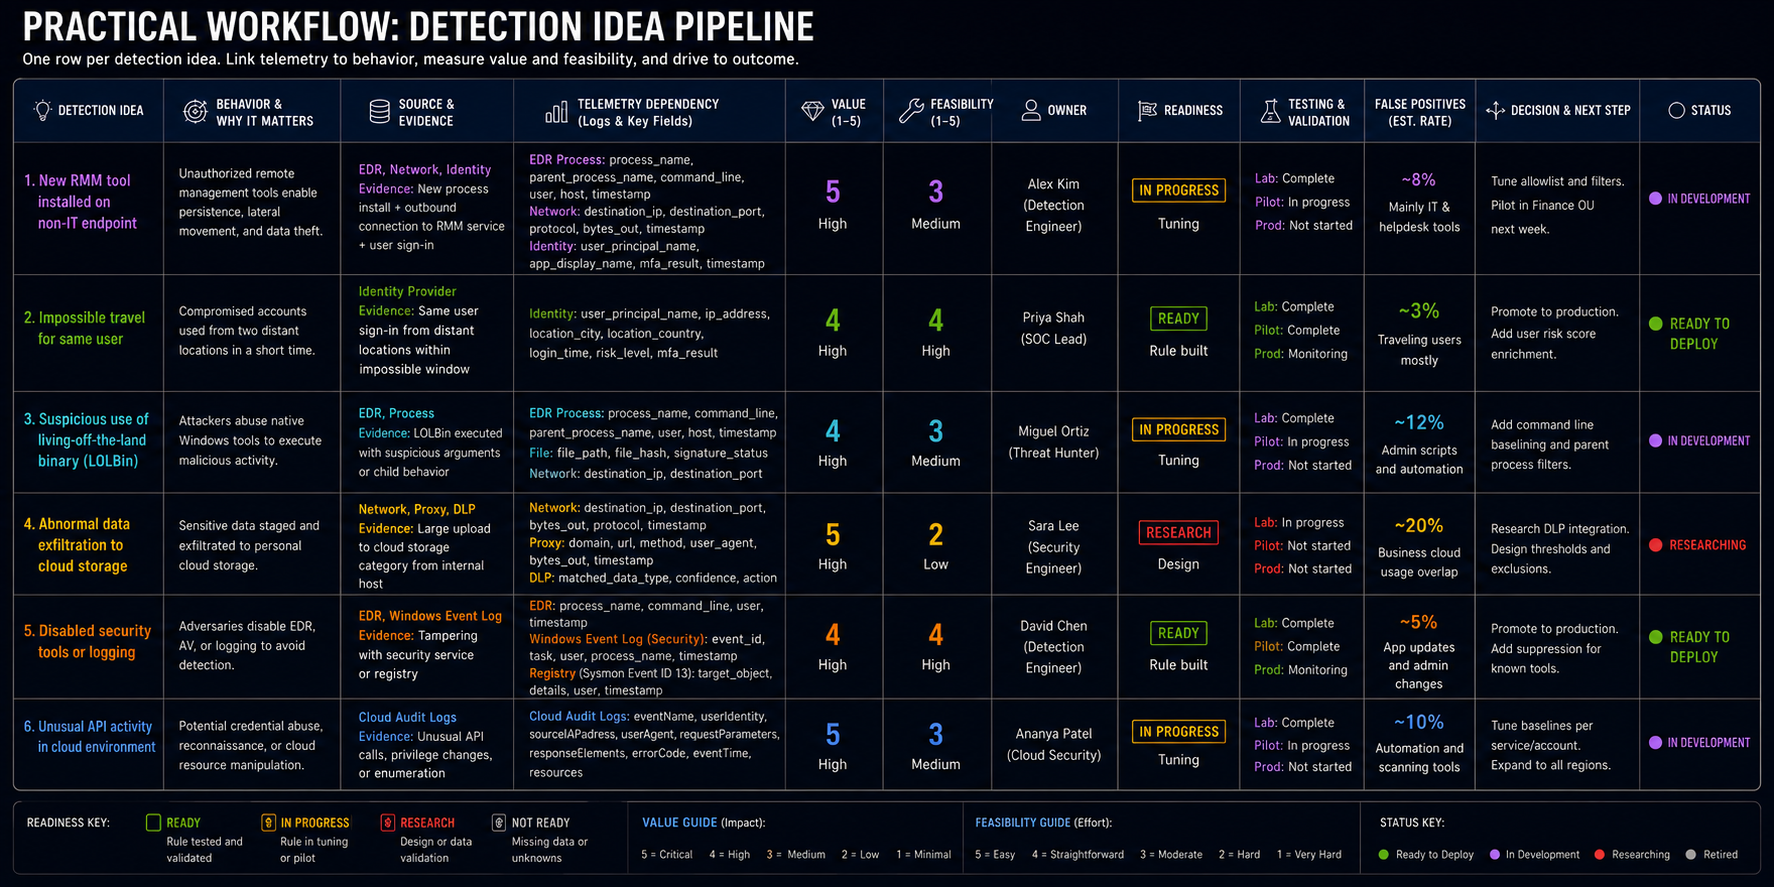
- Jumping from actor report to production alert.
- Skipping telemetry requirements.
- Ignoring false positives and tuning.
- Claiming coverage without validation.
Practical Workflow
- Extract behavior from source reporting.
- Label evidence and confidence.
- Assess environment relevance.
- Define required telemetry and fields.
- Write a testable hunt hypothesis.
- Baseline benign behavior.
- Draft detection logic.
- Validate positive and negative cases.
- Create SOC handoff.
- Assign detection readiness level.
Example / Mini Case
Reported behavior: archive attachment leads to script execution and external download. Detection chain: email attachment metadata, endpoint archive extraction, script process creation, network connection, false-positive baseline for admin scripts, SOC triage instructions.
Analyst Checklist
- Is there a source-backed behavior?
- Is telemetry available?
- Is the hypothesis testable?
- Are false positives named?
- Is readiness level honest?
Output Artifact
Source Claim:
Evidence Label:
Behavior:
Telemetry:
Fields:
Hunt Hypothesis:
Detection Logic:
False Positives:
Validation:
SOC Action:
Readiness Level:
Cross-Links
- Telemetry Requirements
- Detection Backlog
- SOC Handoff
- Customer-Driven AI CTI Project
- Operation Desert Hydra — Full CTI-to-Detection Pipeline (MuddyWater)
Live Example: Operation Desert Hydra
github.com/anpa1200/operation-desert-hydra — a complete, deployable implementation of the workflow on this page: 8 public sources → evidence labels → 10 procedure records → OpenCTI graph → 11 detections → Ansible lab validation → 12 Kibana proof screenshots → coverage matrix. Sigma rules, KQL, Elastic JSON, and SPL are all version-controlled in detections/.
git clone https://github.com/anpa1200/operation-desert-hydra.git
cd operation-desert-hydra
cp stack/.env.template stack/.env
bash start.sh   # OpenCTI :8080 · Kibana :5601 · all 11 simulations
bash stop.sh    # halt; --destroy-vm to remove disk