- AN1452 · Analytic 1452 — Detection of processes executing system environment inspection operations followed by access to OS configuration APIs or registry locations that expose OS version, architecture, patch level, or hardware characteristics. Defenders observe process execution retrieving system configuration metadata immediately after process startup.
- AN1453 · Analytic 1453 — Execution of system enumeration commands such as `uname`, `df`, `uptime`, `hostname`, `lscpu`, and `cat /etc/os-release` through local terminal or scripts.
- AN1454 · Analytic 1454 — Execution of system info utilities like `systemsetup`, `sw_vers`, `uname`, or `sysctl` by terminal or scripted processes.
- AN1455 · Analytic 1455 — Execution of `esxcli system hostname get`, `esxcli system version get`, or `esxcli hardware` commands through SSH or local shell.
- AN1456 · Analytic 1456 — Use of cloud API calls (e.g., AWS EC2 DescribeInstances, Azure VM Inventory) to enumerate system configurations across assets.
- AN1457 · Analytic 1457 — Execution of `show version`, `show hardware`, or `show system` commands through CLI via SSH or console.
AdversaryGraph public intelligence page
This page is part of Threat Matrix, the public browser workspace for the main AdversaryGraph platform. Use it for ATT&CK pivots, actor and technique context, similarity leads, detection coverage review, and analyst-ready investigation paths.
Validation disclaimer: TTP overlap, actor similarity, generated summaries, and coverage findings are investigation leads, not attribution proof or operational validation without analyst review.
Main AdversaryGraph project Documentation Malware Analysis GitHub
System Information Discovery
An adversary may attempt to get detailed information about the operating system and hardware, including version, patches, hotfixes, service packs, and architecture. Adversaries may use this information to shape follow-on behaviors, including whether or not the adversary fully infects the target and/or attempts specific actions. This behavior is distinct from [Local Storage Discovery](https://attack.mitre.org/techniques/T1680) which is an adversary's discovery of local drive, disks and/or volumes. Tools such as [Systeminfo](https://attack.mitre.org/software/S0096) can be used to gather detailed system information. If running with privileged access, a breakdown of system data can be gathered through the <code>systemsetup</code> configuration tool on macOS. Adversaries may leverage a [Network Device CLI](https://attack.mitre.org/techniques/T1059/008) on network devices to gather detailed system information (e.g. <code>show version</code>).(Citation: US-CERT-TA18-106A) On ESXi servers, threat actors may gather system information from various esxcli utilities, such as `system hostname get` and `system version get`.(Citation: Crowdstrike Hypervisor Jackpotting Pt 2 2021)(Citation: Varonis) Infrastructure as a Service (IaaS) cloud providers such as AWS, GCP, and Azure allow access to instance and virtual machine information via APIs. Successful authenticated API calls can return data such as the operating system platform and status of a particular instance or the model view of a virtual machine.(Citation: Amazon Describe Instance)(Citation: Google Instances Resource)(Citation: Mi…
Open detection, hunting, mitigation, and evidence workspace
Detection logic
System and network discovery techniques normally occur throughout an operation as an adversary learns the environment. Data and events should not be viewed in isolation, but as part of a chain of behavior that could lead to other activities based on the information obtained. Monitor processes and command-line arguments for actions that could be taken to gather system and network information. Remote access tools with built-in features may interact directly with the Windows API to gather information. Further, Network Device CLI commands may also be used to gather detailed system information with built-in features native to the network device platform. Monitor CLI activity for unexpected or unauthorized use commands being run by non-standard users from non-standard locations. Information may also be acquired through Windows system management tools such as Windows Management Instrumentation and PowerShell. In cloud-based systems, native logging can be used to identify access to certain APIs and dashboards that may contain system information. Depending on how the environment is used, that data alone may not be useful due to benign use during normal operations.
Observed actors
Ke3chang
G0004Turla
G0010Darkhotel
G0012admin@338
G0018APT3
G0022APT18
G0026Lazarus Group
G0032Sandworm Team
G0034Stealth Falcon
G0038Patchwork
G0040FIN7
G0046Gamaredon Group
G0047OilRig
G0049APT32
G0050Sowbug
G0054Magic Hound
G0059FIN8
G0061APT37
G0067MuddyWater
G0069APT19
G0073Tropic Trooper
G0081APT38
G0082Kimsuky
G0094APT41
G0096Inception
G0100Wizard Spider
G0102Rocke
G0106Blue Mockingbird
G0108Windshift
G0112Sidewinder
G0121Windigo
G0124Higaisa
G0126ZIRCONIUM
G0128Mustang Panda
G0129TeamTNT
G0139Aquatic Panda
G0143HEXANE
G1001SideCopy
G1008Moses Staff
G1009CURIUM
G1012Scattered Spider
G1015FIN13
G1016TA2541
G1018Mustard Tempest
G1020Malteiro
G1026Daggerfly
G1034Winter Vivern
G1035Moonstone Sleet
G1036RedCurl
G1039Play
G1040BlackByte
G1043APT42
G1044Salt Typhoon
G1045Medusa Group
G1051Contagious Interview
G1052Storm-0501
G1053MirrorFace
G1054VOID MANTICORE
G1055ShinyHunters
G1057
Correlated CTI and IR reports
APT39 (Chafer / Remix Kitten)
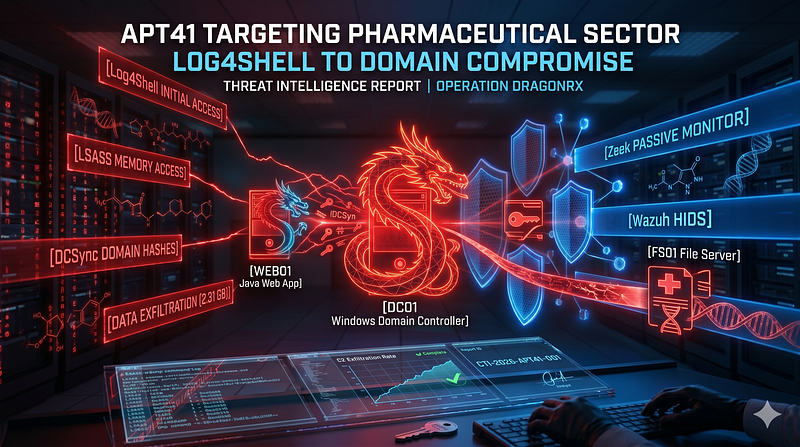
Israel Threat Actors CTI · explicit report mentionAPT41 Targeting Pharmaceutical Sector: Log4Shell to Domain Compromise
1200km CTI repository · explicit report mentionATT&CK as a Working Tool: Theory and Hands-On Practical Usage
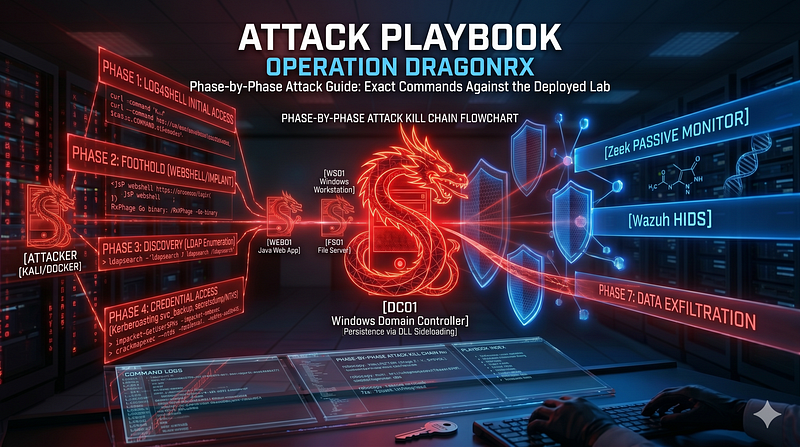
1200km CTI repository · explicit report mentionAttack Playbook — Operation DragonRx
1200km CTI repository · explicit report mentionExecutive Summary
Israel Threat Actors CTI · explicit report mentionOperation DragonRx — APT41 Full Attack Simulation
1200km CTI repository · explicit report mentionOperation DragonRx: Simulating an APT41 Attack End-to-End — From Log4Shell to DFIR and Malware Analysis
1200km CTI repository · explicit report mentionAPT41 Targeting Pharmaceutical Sector Log4Shell to Domain Compromise
1200km Medium · authored report mentionATT CK as a Working Tool Theory and Hands On Practical Usage
1200km Medium · authored report mentionAttack Playbook Operation DragonRx
1200km Medium · authored report mentionOperation DragonRx Simulating an APT41 Attack End to End From Log4Shell to DFIR and Malware
1200km Medium · authored report mention
Cyber Knowledge context
Use these routes to move from the ATT&CK behavior into explanation, implementation, evidence handling, validation, and defensive operations. Relevance is generated from explicit identifiers/names and governed topic mappings; it is not attribution evidence.
Secure AI development lifecycle and production release gate
AI Security · Governed topic match · 60/100Module 6 — Alert triage, investigation, and escalation
Blue Team & Defensive Security · Governed topic match · 54/100Memory forensics and runtime reconstruction
Digital Forensics & Incident Response (DFIR) · Governed topic match · 51/100Internet exposure, service indexes, and infrastructure search
OSINT & Reconnaissance · Tactic learning route · 24/100Module 5 — Cloud, containers, and Kubernetes
Red Team & Offensive Security · Tactic learning route · 24/100Data classification, storage, cryptography, keys, backup, and deletion
Cloud Security · Tactic learning route · 24/100
MITRE mitigations
No ATT&CK mitigation relationship is published for this technique. Apply risk-based controls and verify scope.
MITRE detection strategies and analytics
Continue the investigation
Attack tools, simulations and detection rules
Follow explicit source relationships into the reference modules. Linked procedures and detectors are not claims of live validation or actor attribution.
- T1082 System Information Discovery simulation — Exact active technique ID
- T1082 detection rules — Exact active technique ID; not actor-specific detector coverage