1200KM / sigma-rule
Non-privileged Usage of Reg or Powershell — Sigma Rule
Sigma rule 8f02c935-effe-45b3-8fc9-ef8696a9e41d. Non-privileged Usage of Reg or Powershell — Sigma Rule. Search for usage of reg or Powershell by non-privileged users to modify service configuration in registry
Rule metadata and linked tags
Author: Teymur Kheirkhabarov (idea), Ryan Plas (rule), oscd.community. Source status: test; severity: high. Source dates: 2020-10-05 / 2024-12-01.
{
  "category": "process_creation",
  "product": "windows"
}
Pinned original Sigma rule · Detection Rule License 1.1
Source SHA-256: c5b8d3088af7a131b84785cdc44dafdaab490e7850eb23c7ff8ad2324ddfc21f
Detection logic
Original source YAML. Source-tag agreement is not proof of complete semantic coverage. This rule has not been compiled for a SIEM backend or validated against live telemetry here.
title: Non-privileged Usage of Reg or Powershell
id: 8f02c935-effe-45b3-8fc9-ef8696a9e41d
status: test
description: Search for usage of reg or Powershell by non-privileged users to modify service configuration in registry
references:
    - https://image.slidesharecdn.com/kheirkhabarovoffzonefinal-181117201458/95/hunting-for-privilege-escalation-in-windows-environment-20-638.jpg
author: Teymur Kheirkhabarov (idea), Ryan Plas (rule), oscd.community
date: 2020-10-05
modified: 2024-12-01
tags:
    - attack.persistence
    - attack.defense-impairment
    - attack.t1112
logsource:
    category: process_creation
    product: windows
detection:
    selection_cli:
        - CommandLine|contains|all:
              - 'reg '
              - 'add'
        - CommandLine|contains:
              - 'powershell'
              - 'set-itemproperty'
              - ' sp '
              - 'new-itemproperty'
    selection_data:
        IntegrityLevel:
            - 'Medium'
            - 'S-1-16-8192'
        CommandLine|contains|all:
            - 'ControlSet'
            - 'Services'
        CommandLine|contains:
            - 'ImagePath'
            - 'FailureCommand'
            - 'ServiceDLL'
    condition: all of selection_*
falsepositives:
    - Unknown
level: high
False positives
- Unknown
Source references
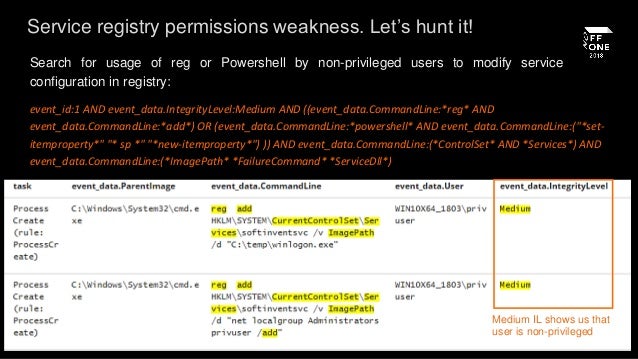
Connected ecosystem references
Exact source-tagged techniques
Telemetry review
Read the original logsource above, then inspect the linked detection workspaces for technique-level sensor context. No per-rule telemetry equivalence is inferred.
Pinned research references. No browser attack runner, live simulation result or validated detector is asserted. Source mappings and validation limits are preserved. ATT&CK / Atomic provenance · Detection provenance.