Use intrusion detection signatures to block traffic at network boundaries.
MITRE mitigation sourceAdversaryGraph public intelligence page
This page is part of Threat Matrix, the public browser workspace for the main AdversaryGraph platform. Use it for ATT&CK pivots, actor and technique context, similarity leads, detection coverage review, and analyst-ready investigation paths.
Validation disclaimer: TTP overlap, actor similarity, generated summaries, and coverage findings are investigation leads, not attribution proof or operational validation without analyst review.
Main AdversaryGraph project Documentation Malware Analysis GitHub
Exfiltration Over C2 Channel
Adversaries may steal data by exfiltrating it over an existing command and control channel. Stolen data is encoded into the normal communications channel using the same protocol as command and control communications.(Citation: C2 FRAMEWORKS)
Open detection, hunting, mitigation, and evidence workspace
Detection logic
Analyze network data for uncommon data flows (e.g., a client sending significantly more data than it receives from a server). Processes utilizing the network that do not normally have network communication or have never been seen before are suspicious. Analyze packet contents to detect communications that do not follow the expected protocol behavior for the port that is being used.
Observed actors
Ke3chang
G0004APT3
G0022Lazarus Group
G0032Sandworm Team
G0034Stealth Falcon
G0038Gamaredon Group
G0047APT32
G0050Leviathan
G0065MuddyWater
G0069APT38
G0082APT39
G0087WIRTE
G0090GALLIUM
G0093Kimsuky
G0094Wizard Spider
G0102Chimera
G0114Higaisa
G0126ZIRCONIUM
G0128Mustang Panda
G0129Confucius
G0142CURIUM
G1012LuminousMoth
G1014Scattered Spider
G1015Agrius
G1030Winter Vivern
G1035BlackByte
G1043Contagious Interview
G1052VOID MANTICORE
G1055
Correlated CTI and IR reports
APT39 (Chafer / Remix Kitten)
Israel Threat Actors CTI · explicit report mentionAPT41 Targeting Pharmaceutical Sector: Log4Shell to Domain Compromise
1200km CTI repository · explicit report mentionAttack Playbook — Operation DragonRx
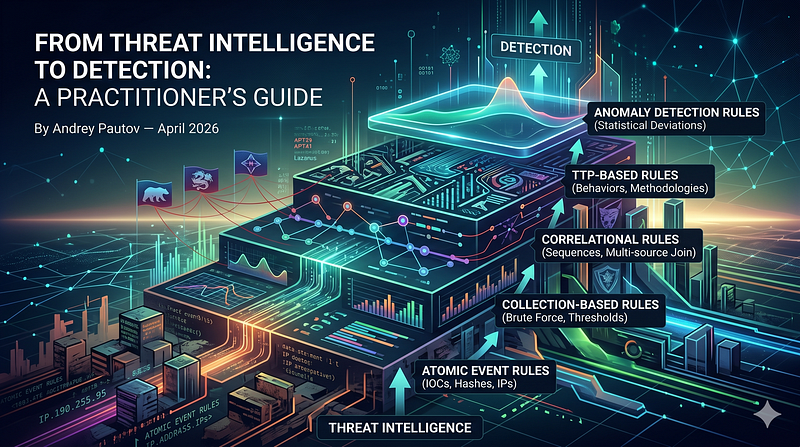
1200km CTI repository · explicit report mentionFrom Threat Intelligence to Detection: A Practitioner's Guide
1200km CTI repository · explicit report mentionOperation DragonRx — APT41 Full Attack Simulation
1200km CTI repository · explicit report mentionOperation DragonRx: Simulating an APT41 Attack End-to-End — From Log4Shell to DFIR and Malware Analysis
1200km CTI repository · explicit report mentionAPT41 Targeting Pharmaceutical Sector Log4Shell to Domain Compromise
1200km Medium · authored report mentionAttack Playbook Operation DragonRx
1200km Medium · authored report mentionCTI Led Defensive Strategy for a Cellular Provider Case Study
1200km Medium · authored report mentionCorrelation Based Detection Rules in Cybersecurity From Atomic Events to Behavioral Insight
1200km Medium · authored report mentionFrom Threat Intelligence to Detection A Practitioner s Guide
1200km Medium · authored report mentionOperation DragonRx Simulating an APT41 Attack End to End From Log4Shell to DFIR and Malware
1200km Medium · authored report mentionSingle Event Detection Rules in Cybersecurity
1200km Medium · authored report mention
Cyber Knowledge context
Use these routes to move from the ATT&CK behavior into explanation, implementation, evidence handling, validation, and defensive operations. Relevance is generated from explicit identifiers/names and governed topic mappings; it is not attribution evidence.
Windows endpoint and identity forensics
Digital Forensics & Incident Response (DFIR) · Tactic learning route · 24/100Module 6 — Alert triage, investigation, and escalation
Blue Team & Defensive Security · Tactic learning route · 24/100Infrastructure as code, CI/CD, artifact provenance, and policy as code
Cloud Security · Tactic learning route · 24/100
MITRE mitigations
Data Loss Prevention (DLP) involves implementing strategies and technologies to identify, categorize, monitor, and control the movement of sensitive data within an organization. This includes protecting data formats indicative of Personally Identifiable Information (PII), intellectual property, or financial data from unauthorized access, transmission, or exfiltration. DLP solutions integrate with network, endpoint, and cloud platforms to enforce security policies and prevent accidental or malicious data leaks. (Citation: PurpleSec Data Loss Prevention) This mitigation can be implemented through the following measures: Sensitive Data Categorization: - Use Case: Identify and classify data based on sensitivity (e.g., PII, financial data, trade secrets). - Implementation: Use DLP solutions to scan and tag files containing sensitive information using predefined patterns, such as Social Secur…
MITRE mitigation sourceMITRE detection strategies and analytics
- AN0988 · Analytic 0988 — Identifies suspicious outbound traffic volume mismatches from processes that typically do not generate network activity, particularly over C2 protocols like HTTPS, DNS, or custom TCP/UDP ports, following file or data access.
- AN0989 · Analytic 0989 — Monitors for processes reading sensitive files then immediately initiating unusual outbound connections or bulk transfer sessions over persistent sockets, particularly with encrypted or binary payloads.
- AN0990 · Analytic 0990 — Detects unauthorized applications or scripts accessing sensitive data followed by establishing encrypted outbound communication to rare external destinations or with abnormal byte ratios.
- AN0991 · Analytic 0991 — Detects VMs sending outbound traffic through non-standard services or to unknown destinations. Exfiltration over reverse shells tunneled via VMkernel or custom payloads routed via hostd/vpxa.
Related sector research
Editorial reading routes, not additional MITRE relationships or proof of an actor's involvement in a particular incident.
- Cyberattacks on Big Pharma and Its Ecosystem — Analytical mapping of LEMURLOOT command-and-output behavior; not labeled as a CISA-assigned victim technique. Evidence cutoff: 2026-09-25.
Continue the investigation
Attack tools, simulations and detection rules
Follow explicit source relationships into the reference modules. Linked procedures and detectors are not claims of live validation or actor attribution.
- T1041 Exfiltration Over C2 Channel simulation — Exact active technique ID
- T1041 detection rules — Exact active technique ID; not actor-specific detector coverage