1200KM / sigma-rule
Always Install Elevated Windows Installer — Sigma Rule
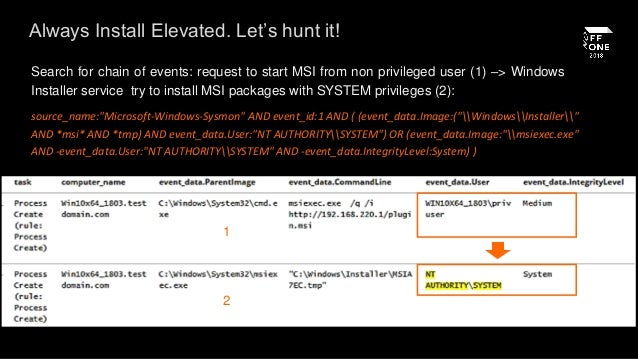
Sigma rule cd951fdc-4b2f-47f5-ba99-a33bf61e3770. Always Install Elevated Windows Installer — Sigma Rule. Detects Windows Installer service (msiexec.exe) trying to install MSI packages with SYSTEM privilege
Rule metadata and linked tags
Author: Teymur Kheirkhabarov (idea), Mangatas Tondang (rule), oscd.community. Source status: test; severity: medium. Source dates: 2020-10-13 / 2024-12-01.
{
  "product": "windows",
  "category": "process_creation"
}
Pinned original Sigma rule · Detection Rule License 1.1
Source SHA-256: 0de11202d557e15231cfc262eb305587764e13dca774f1c2a619584ea8b35d5b
Detection logic
Original source YAML. Source-tag agreement is not proof of complete semantic coverage. This rule has not been compiled for a SIEM backend or validated against live telemetry here.
title: Always Install Elevated Windows Installer
id: cd951fdc-4b2f-47f5-ba99-a33bf61e3770
status: test
description: Detects Windows Installer service (msiexec.exe) trying to install MSI packages with SYSTEM privilege
references:
    - https://image.slidesharecdn.com/kheirkhabarovoffzonefinal-181117201458/95/hunting-for-privilege-escalation-in-windows-environment-48-638.jpg
author: Teymur Kheirkhabarov (idea), Mangatas Tondang (rule), oscd.community
date: 2020-10-13
modified: 2024-12-01
tags:
    - attack.privilege-escalation
    - attack.t1548.002
logsource:
    product: windows
    category: process_creation
detection:
    selection_user:
        User|contains: # covers many language settings
            - 'AUTHORI'
            - 'AUTORI'
    selection_image_1:
        Image|contains|all:
            - '\Windows\Installer\'
            - 'msi'
        Image|endswith: 'tmp'
    selection_image_2:
        Image|endswith: '\msiexec.exe'
        IntegrityLevel:
            - 'System'
            - 'S-1-16-16384'
    filter_installer:
        ParentImage: 'C:\Windows\System32\services.exe'
    filter_repair:
        - CommandLine|endswith: '\system32\msiexec.exe /V' # ignore "repair option"
        - ParentCommandLine|endswith: '\system32\msiexec.exe /V' # ignore "repair option"
    filter_sophos:
        ParentImage|startswith: 'C:\ProgramData\Sophos\'
    filter_avira:
        ParentImage|startswith: 'C:\ProgramData\Avira\'
    filter_avast:
        ParentImage|startswith:
            - 'C:\Program Files\Avast Software\'
            - 'C:\Program Files (x86)\Avast Software\'
    filter_google_update:
        ParentImage|startswith:
            - 'C:\Program Files\Google\Update\'
            - 'C:\Program Files (x86)\Google\Update\'
    condition: 1 of selection_image_* and selection_user and not 1 of filter_*
falsepositives:
    - System administrator usage
    - Anti virus products
    - WindowsApps located in "C:\Program Files\WindowsApps\"
level: medium
False positives
- System administrator usage
- Anti virus products
- WindowsApps located in "C:\Program Files\WindowsApps\"
Source references
Connected ecosystem references
Exact source-tagged techniques
Telemetry review
Read the original logsource above, then inspect the linked detection workspaces for technique-level sensor context. No per-rule telemetry equivalence is inferred.
Pinned research references. No browser attack runner, live simulation result or validated detector is asserted. Source mappings and validation limits are preserved. ATT&CK / Atomic provenance · Detection provenance.