1200KM / sigma-rule
HackTool - Credential Dumping Tools Named Pipe Created — Sigma Rule
Sigma rule 961d0ba2-3eea-4303-a930-2cf78bbfcc5e. HackTool - Credential Dumping Tools Named Pipe Created — Sigma Rule. Detects well-known credential dumping tools execution via specific named pipe creation
Rule metadata and linked tags
Author: Teymur Kheirkhabarov, oscd.community. Source status: test; severity: critical. Source dates: 2019-11-01 / 2023-08-07.
{
  "product": "windows",
  "category": "pipe_created",
  "definition": "Note that you have to configure logging for Named Pipe Events in Sysmon config (Event ID 17 and Event ID 18). The basic configuration is in popular sysmon configuration (https://github.com/SwiftOnSecurity/sysmon-config), but it is worth verifying. You can also use other repo, e.g. https://github.com/Neo23x0/sysmon-config, https://github.com/olafhartong/sysmon-modular. How to test detection? You can check powershell script from this site https://svch0st.medium.com/guide-to-named-pipes-and-hunting-for-cobalt-strike-pipes-dc46b2c5f575"
}
Pinned original Sigma rule · Detection Rule License 1.1
Source SHA-256: bbc77c9aec5e669815440da6f0e7cf7372b965eca9dafce68e345daed1876e95
Detection logic
Original source YAML. Source-tag agreement is not proof of complete semantic coverage. This rule has not been compiled for a SIEM backend or validated against live telemetry here.
title: HackTool - Credential Dumping Tools Named Pipe Created
id: 961d0ba2-3eea-4303-a930-2cf78bbfcc5e
status: test
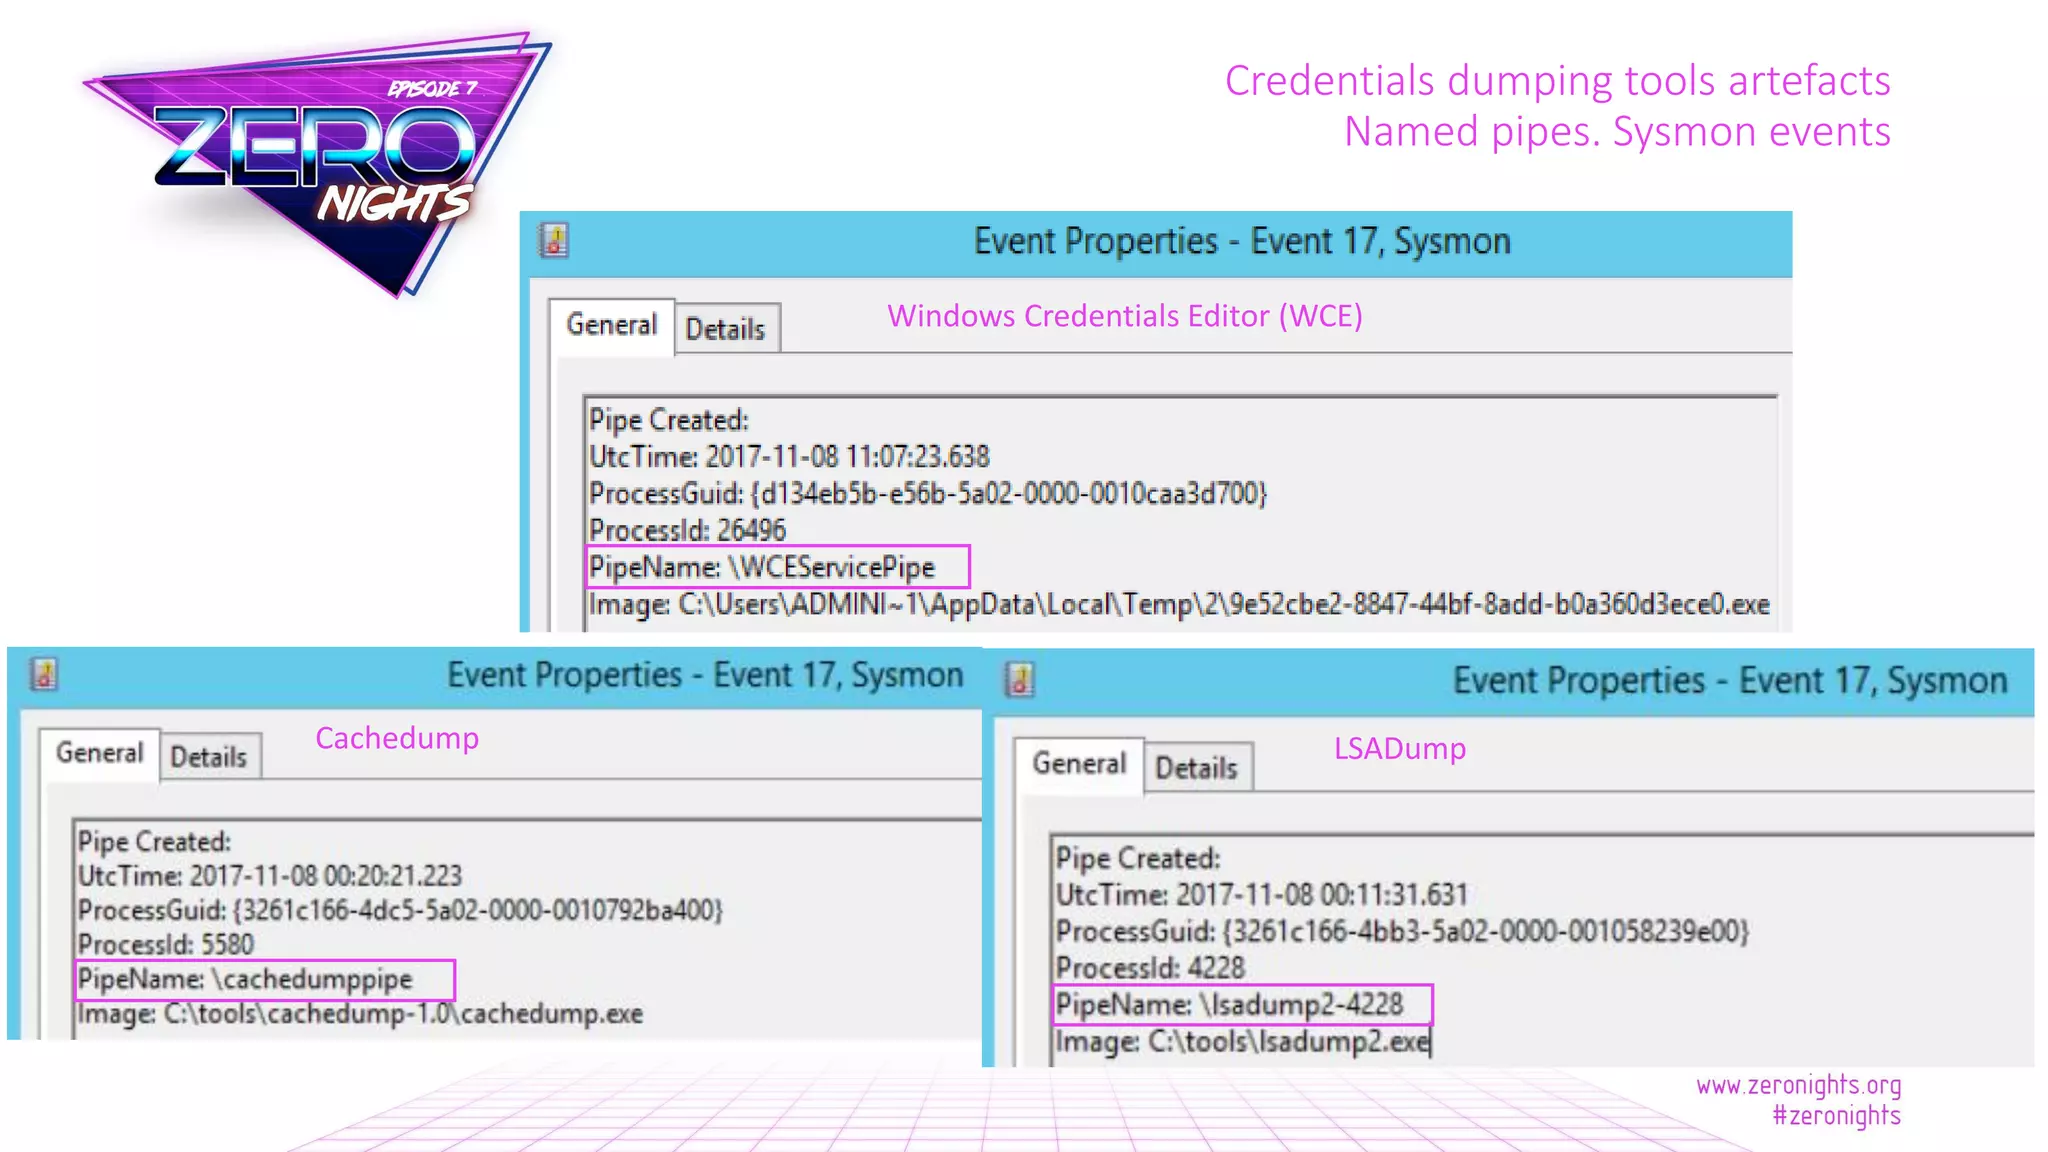
description: Detects well-known credential dumping tools execution via specific named pipe creation
references:
    - https://www.slideshare.net/heirhabarov/hunting-for-credentials-dumping-in-windows-environment
    - https://image.slidesharecdn.com/zeronights2017kheirkhabarov-171118103000/75/hunting-for-credentials-dumping-in-windows-environment-57-2048.jpg?cb=1666035799
author: Teymur Kheirkhabarov, oscd.community
date: 2019-11-01
modified: 2023-08-07
tags:
    - attack.credential-access
    - attack.t1003.001
    - attack.t1003.002
    - attack.t1003.004
    - attack.t1003.005
logsource:
    product: windows
    category: pipe_created
    definition: 'Note that you have to configure logging for Named Pipe Events in Sysmon config (Event ID 17 and Event ID 18). The basic configuration is in popular sysmon configuration (https://github.com/SwiftOnSecurity/sysmon-config), but it is worth verifying. You can also use other repo, e.g. https://github.com/Neo23x0/sysmon-config, https://github.com/olafhartong/sysmon-modular. How to test detection? You can check powershell script from this site https://svch0st.medium.com/guide-to-named-pipes-and-hunting-for-cobalt-strike-pipes-dc46b2c5f575'
detection:
    selection:
        PipeName|contains:
            - '\cachedump'
            - '\lsadump'
            - '\wceservicepipe'
    condition: selection
falsepositives:
    - Legitimate Administrator using tool for password recovery
level: critical
False positives
- Legitimate Administrator using tool for password recovery
Source references
Connected ecosystem references
Exact source-tagged techniques
Telemetry review
Read the original logsource above, then inspect the linked detection workspaces for technique-level sensor context. No per-rule telemetry equivalence is inferred.
Pinned research references. No browser attack runner, live simulation result or validated detector is asserted. Source mappings and validation limits are preserved. ATT&CK / Atomic provenance · Detection provenance.