
Restricting web-based content involves enforcing policies and technologies that limit access to potentially malicious websites, unsafe downloads, and unauthorized browser behaviors. This can include URL filtering, download restrictions, script blocking, and extension control to protect against exploitation, phishing, and malware delivery. This mitigation can be implemented through the following measures: Deploy Web Proxy Filtering: - Use solutions to filter web traffic based on categories, reputation, and content types. - Enforce policies that block unsafe websites or file types at the gateway level. Enable DNS-Based Filtering: - Implement tools to restrict access to domains associated with malware or phishing campaigns. - Use public DNS filtering services to enhance protection. Enforce Content Security Policies (CSP): - Configure CSP headers on internal and external web applications to…
MITRE mitigation sourceAdversaryGraph public intelligence page
This page is part of Threat Matrix, the public browser workspace for the main AdversaryGraph platform. Use it for ATT&CK pivots, actor and technique context, similarity leads, detection coverage review, and analyst-ready investigation paths.
Validation disclaimer: TTP overlap, actor similarity, generated summaries, and coverage findings are investigation leads, not attribution proof or operational validation without analyst review.
Main AdversaryGraph project Documentation Malware Analysis GitHub
Exfiltration to Cloud Storage
Adversaries may exfiltrate data to a cloud storage service rather than over their primary command and control channel. Cloud storage services allow for the storage, edit, and retrieval of data from a remote cloud storage server over the Internet. Examples of cloud storage services include Dropbox and Google Docs. Exfiltration to these cloud storage services can provide a significant amount of cover to the adversary if hosts within the network are already communicating with the service.
Open detection, hunting, mitigation, and evidence workspace
Detection logic
Analyze network data for uncommon data flows (e.g., a client sending significantly more data than it receives from a server) to known cloud storage services. Processes utilizing the network that do not normally have network communication or have never been seen before are suspicious. User behavior monitoring may help to detect abnormal patterns of activity.
Observed actors
G0010Threat Group-3390
G0027FIN7
G0046Leviathan
G0065MuddyWater
G0069Kimsuky
G0094Wizard Spider
G0102Chimera
G0114Indrik Spider
G0119HAFNIUM
G0125ZIRCONIUM
G0128Mustang Panda
G0129Confucius
G0142HEXANE
G1001Ember Bear
G1003POLONIUM
G1005Earth Lusca
G1006LuminousMoth
G1014Scattered Spider
G1015Cinnamon Tempest
G1021ToddyCat
G1022Akira
G1024Medusa Group
G1051Contagious Interview
G1052Storm-0501
G1053
Correlated CTI and IR reports
Unit 42 · direct source mappingStryker Handala MOIS and MuddyWater: Full Kill Chain and Unified Detection Pack v3
ThreatHunter.ai · direct source mappingCTI Research: Handala Hack Group (aka Handala Hack Team)
1200km CTI repository · explicit report mentionCTI Research: Handala Hack Group (aka Handala Hack Team)
1200km CTI repository · explicit report mentionDefensive Cyber Threat Intelligence Report: Israeli Critical Infrastructure and Geopolitical Escalation (2024-2026)
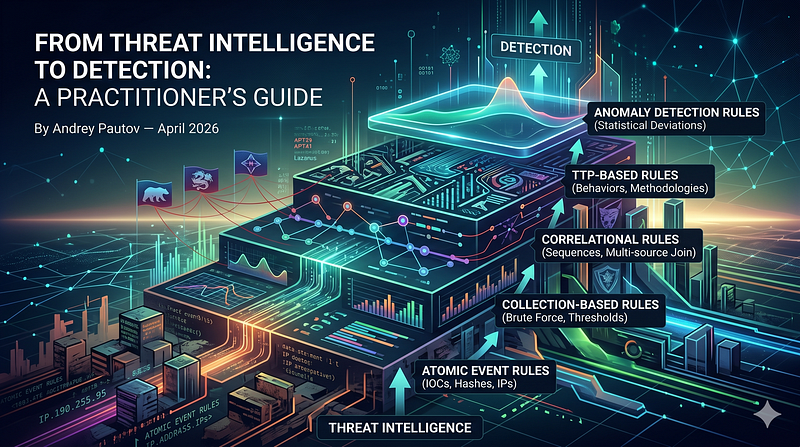
Israel Threat Actors CTI · explicit report mentionFrom Threat Intelligence to Detection: A Practitioner's Guide
1200km CTI repository · explicit report mentionOilRig (APT34 / Helix Kitten / Earth Simnavaz etc)
Israel Threat Actors CTI · explicit report mentionCTI Research Handala Hack Group aka Handala Hack Team
1200km Medium · authored report mentionFrom Threat Intelligence to Detection A Practitioner s Guide
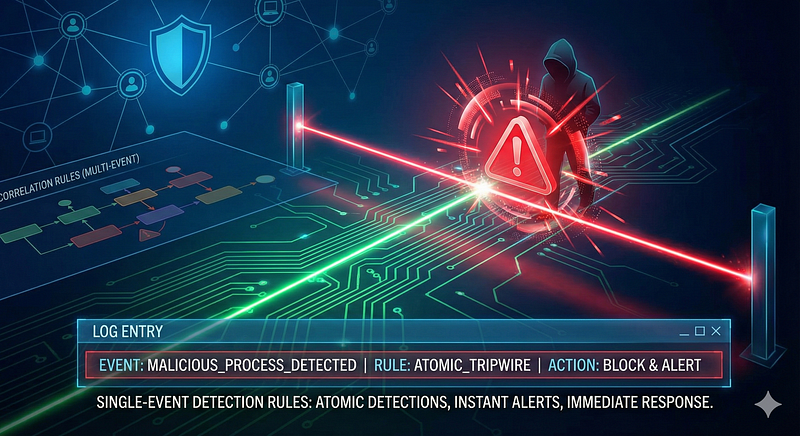
1200km Medium · authored report mentionSingle Event Detection Rules in Cybersecurity
1200km Medium · authored report mention
Cyber Knowledge context
Use these routes to move from the ATT&CK behavior into explanation, implementation, evidence handling, validation, and defensive operations. Relevance is generated from explicit identifiers/names and governed topic mappings; it is not attribution evidence.
Digital Forensics & Incident Response (DFIR) · Tactic learning route · 24/100Module 6 — Alert triage, investigation, and escalation
Blue Team & Defensive Security · Tactic learning route · 24/100Infrastructure as code, CI/CD, artifact provenance, and policy as code
Cloud Security · Tactic learning route · 24/100
MITRE mitigations
MITRE detection strategies and analytics
- AN1571 · Analytic 1571 — Unusual processes (e.g., powershell.exe, excel.exe) accessing large local files and subsequently initiating HTTPS POST requests to domains associated with cloud storage services (e.g., dropbox.com, drive.google.com, box.com). Defender perspective: correlation between file reads in sensitive directories and high outbound traffic volume to known storage APIs.
- AN1572 · Analytic 1572 — Processes such as curl, wget, rclone, or custom scripts executing uploads to cloud storage endpoints. Defender perspective: detect chained events where tar/gzip is executed to compress files followed by HTTPS PUT/POST requests to known storage services.
- AN1573 · Analytic 1573 — Applications or scripts invoking cloud storage APIs (Dropbox sync, iCloud, Google Drive client) in unexpected contexts. Defender perspective: detect sensitive file reads by non-standard applications followed by unusual encrypted uploads to external cloud storage domains.
- AN1574 · Analytic 1574 — Unusual ESXi processes (vmx, hostd) reading datastore files and generating outbound HTTPS traffic toward external cloud storage endpoints. Defender perspective: anomalous datastore activity followed by network transfers to Dropbox, AWS S3, or other storage services.
Continue the investigation
Attack tools, simulations and detection rules
Follow explicit source relationships into the reference modules. Linked procedures and detectors are not claims of live validation or actor attribution.
- T1567.002 Exfiltration to Cloud Storage simulation — Exact active technique ID
- T1567.002 detection rules — Exact active technique ID; not actor-specific detector coverage